Projects
Selected work, sanitized for public sharing. No real addresses, account names or configs.
ENTERPRISE VIRTUALIZATION HOMELAB
A Dell PowerEdge R520 running Proxmox with about 25 VMs and containers, ZFS RAID-Z storage and iDRAC for out-of-band management. This month I moved it off an end-of-life release to Proxmox 9 using a written runbook: fresh backups, pre-flight checks, clean shutdowns, a rollback plan. Everything came back and got verified afterward. Along the way I found a storage cache quietly eating half the host's memory, and cut backups from 6 TB of nightly copies to about 0.4 TB of weekly ones that cover what actually matters.
▸ SEE SCREENSHOTSZERO-TRUST ACCESS & PERIMETER
OPNsense at the edge: default-deny, IDS, geo-blocking, DNS filtering. Remote access goes through Twingate, and public services go out through an outbound-only tunnel to a cloud relay, so neither one needs an open inbound port at home. I hardened the remote-access box (host firewall, key-only SSH, removed file sharing nobody needed) and re-scanned it with Nessus: 0 open ports, 0 findings. VLAN segmentation is designed and the migration is underway, one host at a time.
▸ SEE SCREENSHOTSEAST-WEST INTRUSION DETECTIONNEW
My edge firewall can't see traffic between VMs on the same host, so I gave that traffic its own sensor. Suricata, detect-only, fed by a virtual SPAN port with a listen-only interface. First real test: a priority-1 MS08-067 alert against my file server. I matched the alert's source port to an authenticated session and confirmed it was a false positive, my own Windows Explorer browsing the shares. Next step is tuning it so that alert stays quiet for my own sessions but still fires for anything else.
▸ SEE SCREENSHOTSLIVE HOMELAB DASHBOARDNEW
One page that shows me everything: host and VM health, who's online on each game server, IDS alerts, drive health (SMART), storage and backup status. It runs inside the lab around the clock, uses a read-only API account and locked-down keys, and refreshes every 15 seconds without hammering the network.
▸ SEE SCREENSHOTS▸ TRY THE DEMOINFRASTRUCTURE AUTOMATION WITH ANSIBLEIN PROGRESS
Building this one by hand on purpose. A dedicated control node, a local Git repo, inventory for the lab. Next up are playbooks for patching and an SSH baseline mapped to DISA STIG rules, applied the way change control expects: dry run with a diff first, then apply.
▸ SEE SCREENSHOTSSELF-HOSTED AI
A single GPU passed through to a VM, running two things. A private chat and document-search setup (Ollama, Open WebUI and a Qdrant vector database), and a real-time voice assistant: speech-to-text, a local language model, then text-to-speech, answering in about two seconds. Nothing leaves the network. A second VM handles local image and video generation.
SELF-HOSTED CHAT SERVERPAST
Built and ran a Matrix chat server (Conduit) with an Element web client, behind a Caddy reverse proxy and published through Cloudflare Tunnel, with TLS end to end and no ports opened at home.
DEDICATED GAME SERVERS
I host four dedicated game servers for a group of friends. Treated like production: scheduled restarts with in-game warnings, weekly backups, scripted mod updates, host firewalls, and players connecting through the tunnel instead of open ports.
STIG COMPLIANCE AUTOMATION
Built a findings database and script that took our DISA STIG scans from hours down to minutes, so the team spent its time fixing findings instead of compiling them.
DATA-CENTER OPERATIONS
Wrote an asset-auditing guideline that bridged a legacy platform, and revamped new-hire onboarding, saving about a week of ramp-up per hire.
CERTIFICATIONS
- CompTIA Security+ (SY0-701), valid through Aug 2027
- Microsoft Azure Fundamentals (AZ-900)
- Cisco CCNP Enterprise, in progress
- B.S. Information Technology, William Paterson University (Honors)
Verify on Credly: credly.com/users/pedro-liranzo · Download résumé (PDF)
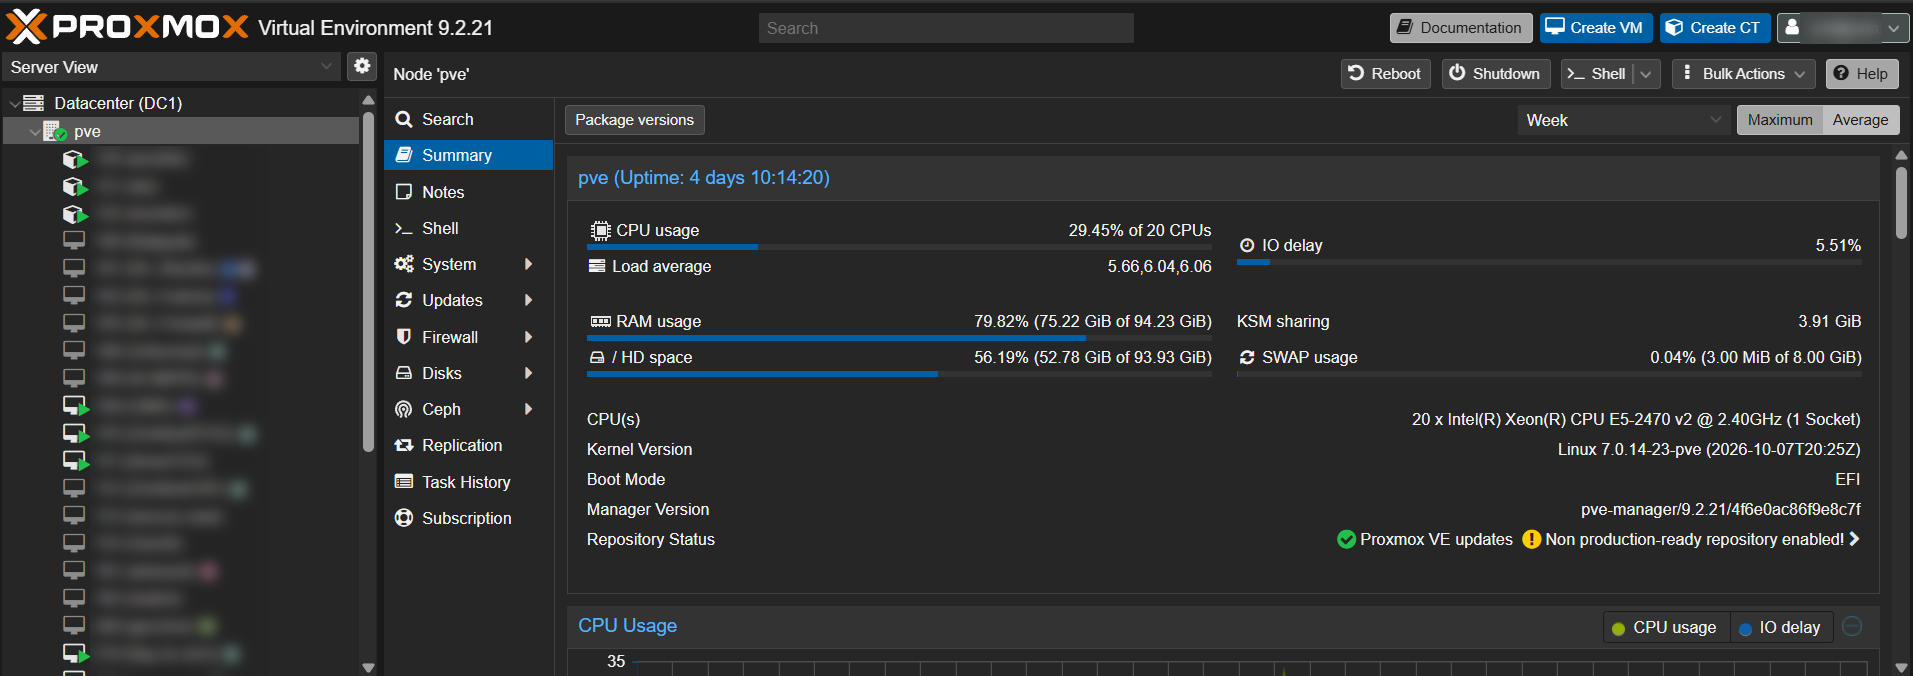
Proxmox VE 9 on a Dell R520: 20 threads, 94 GB RAM, about 25 VMs and containers. Moved off an end-of-life release with a written runbook and rollback plan. (VM names blurred.)
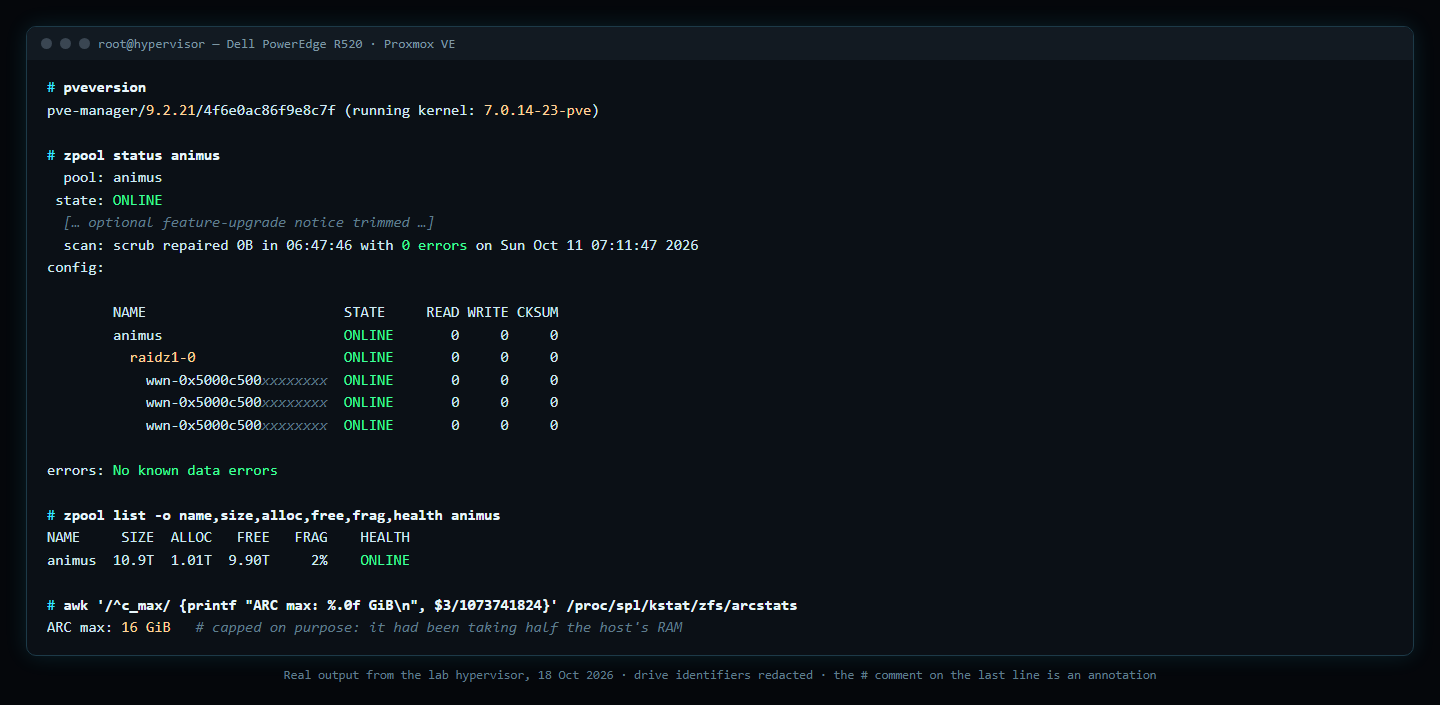
ZFS RAID-Z pool healthy, 0 scrub errors. ARC cache capped at 16 GB after I found it quietly eating half the host's memory. (Drive IDs redacted.)
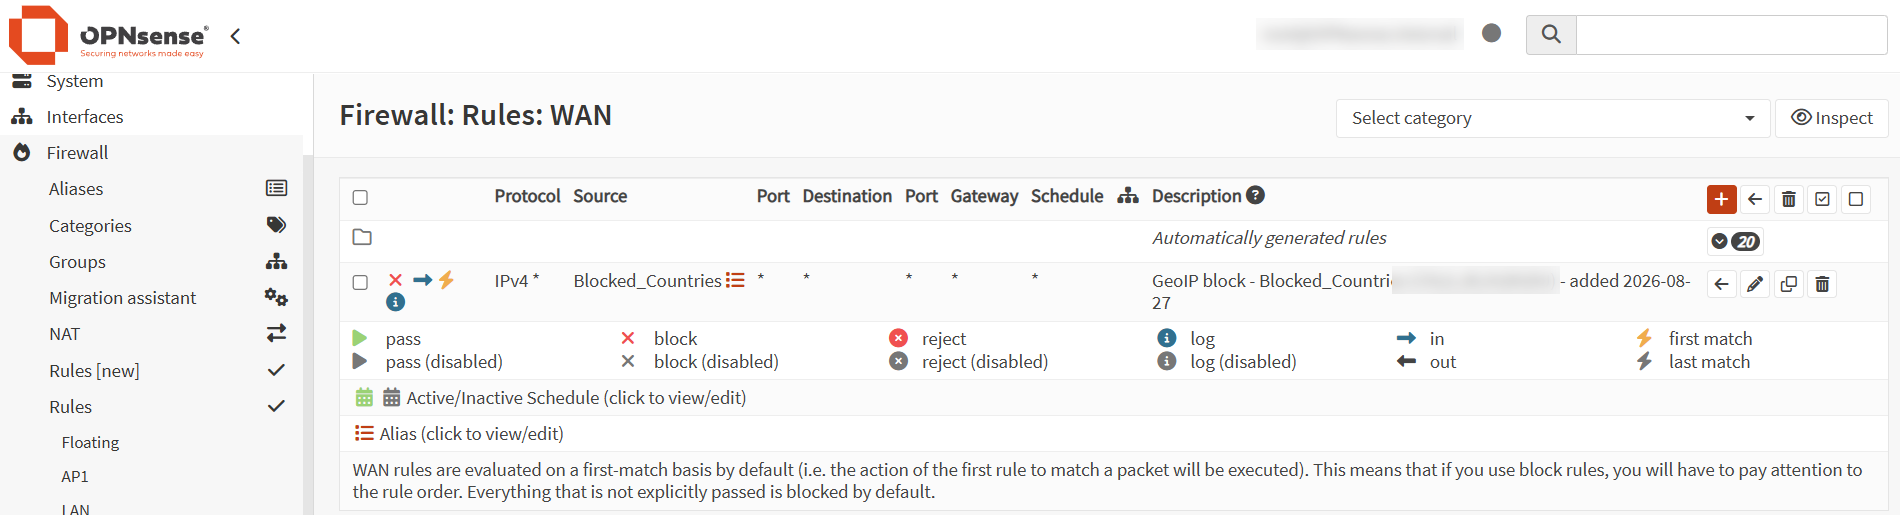
Edge firewall WAN rules after I retired every inbound port-forward: geo-block on top, everything else denied by default. Players reach the game servers through an outbound-only tunnel. Verified closed from outside.
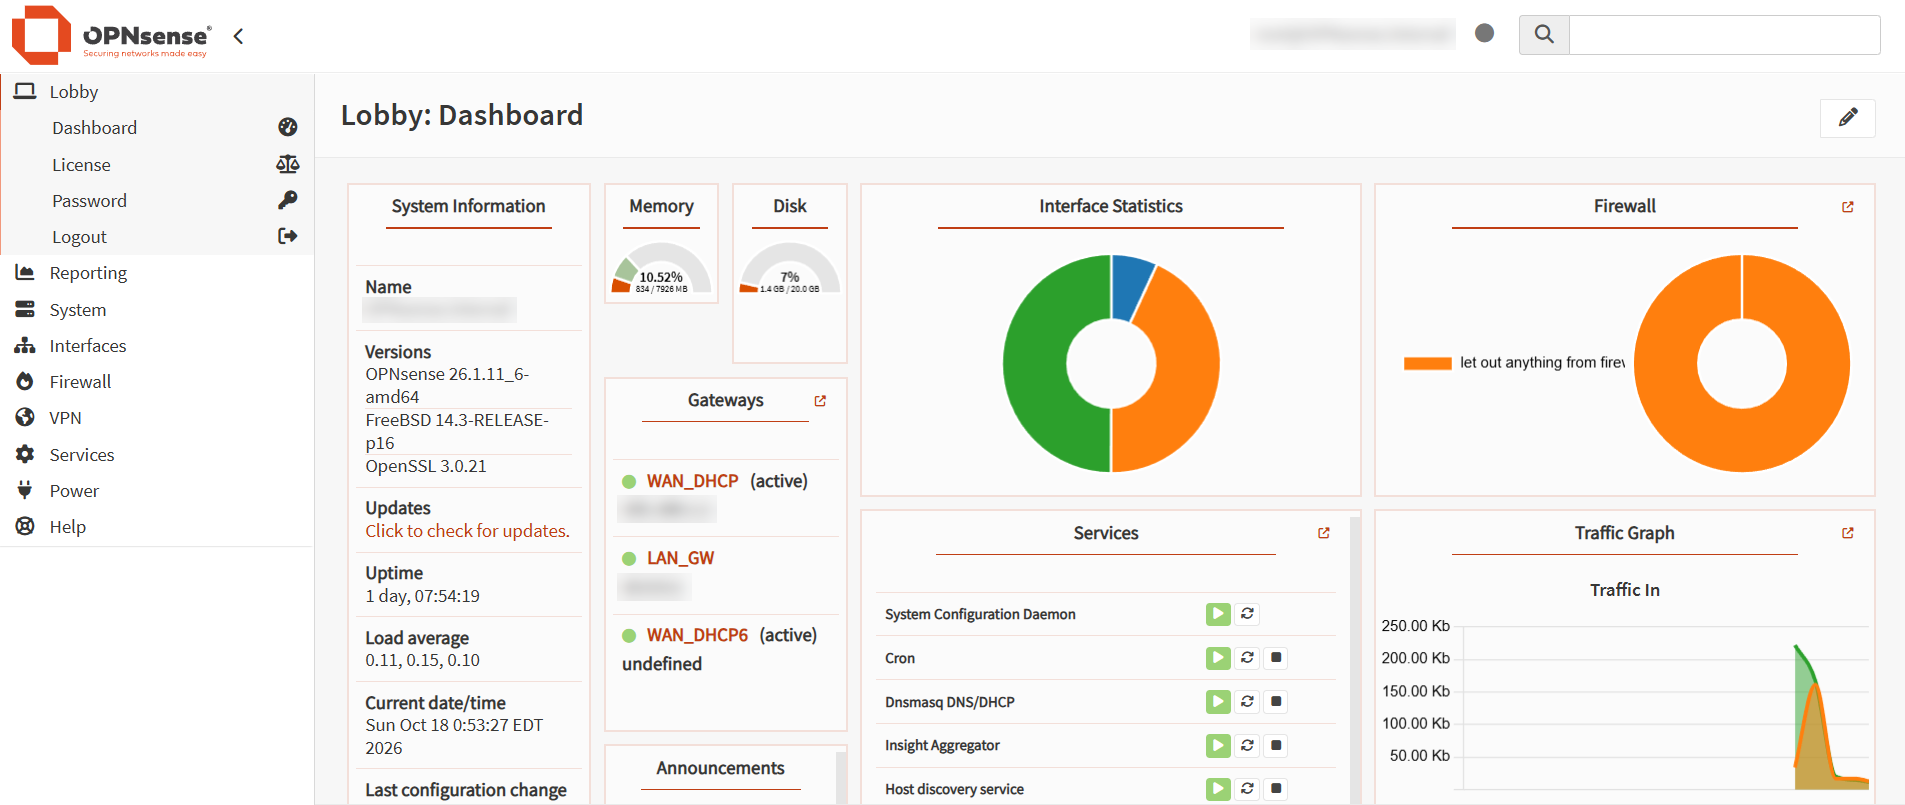
OPNsense at the edge: current release, services healthy, live traffic. (Hostname and gateway addresses blurred.)
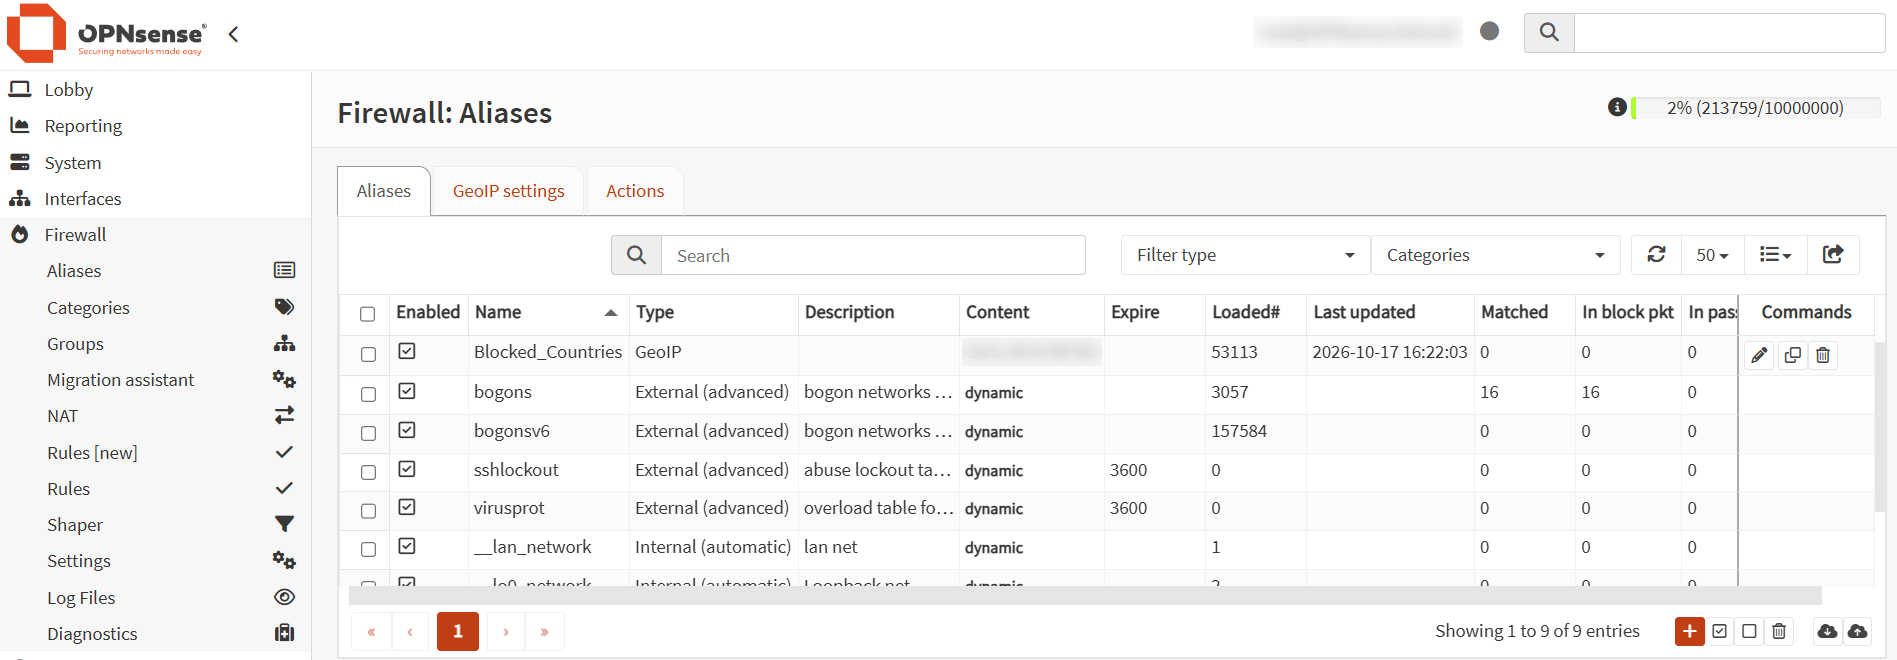
Geo-blocking plus bogon and abuse-lockout tables doing their job: 16 bogon packets already dropped. (Country list blurred.)
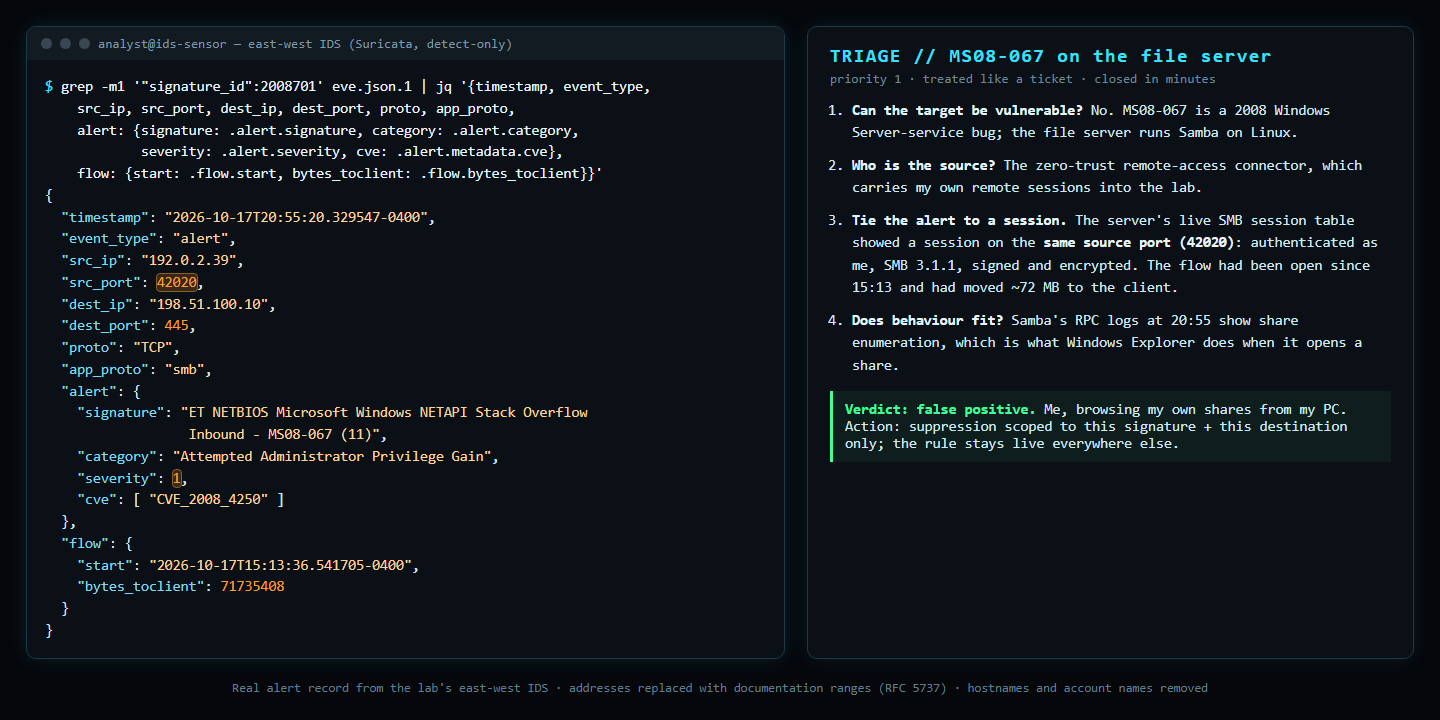
My first real priority-1 IDS alert (MS08-067 against the file server) and the evidence chain that proved it was a false positive. Real alert record; addresses swapped for documentation ranges.
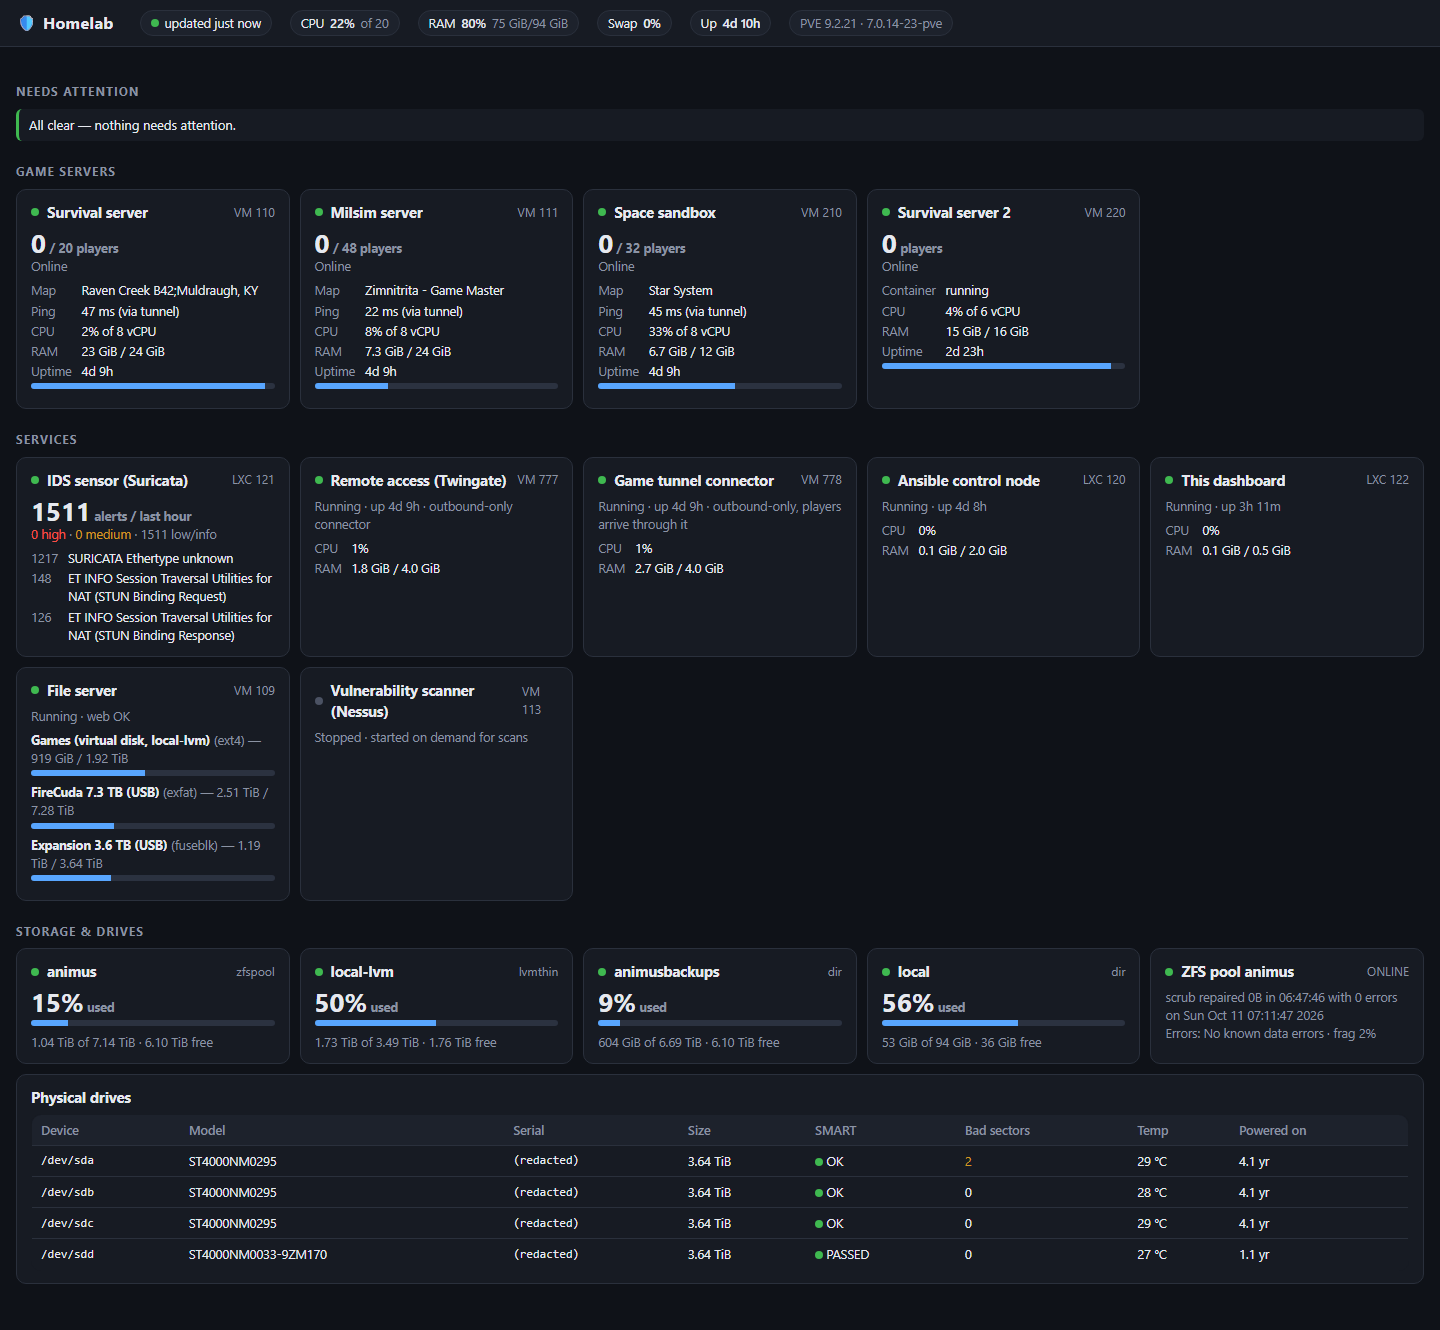
The live dashboard I built: game servers, IDS alerts, drive health (SMART) and storage, refreshed every 15 seconds through a read-only API account. Real numbers, identifying names scrubbed.
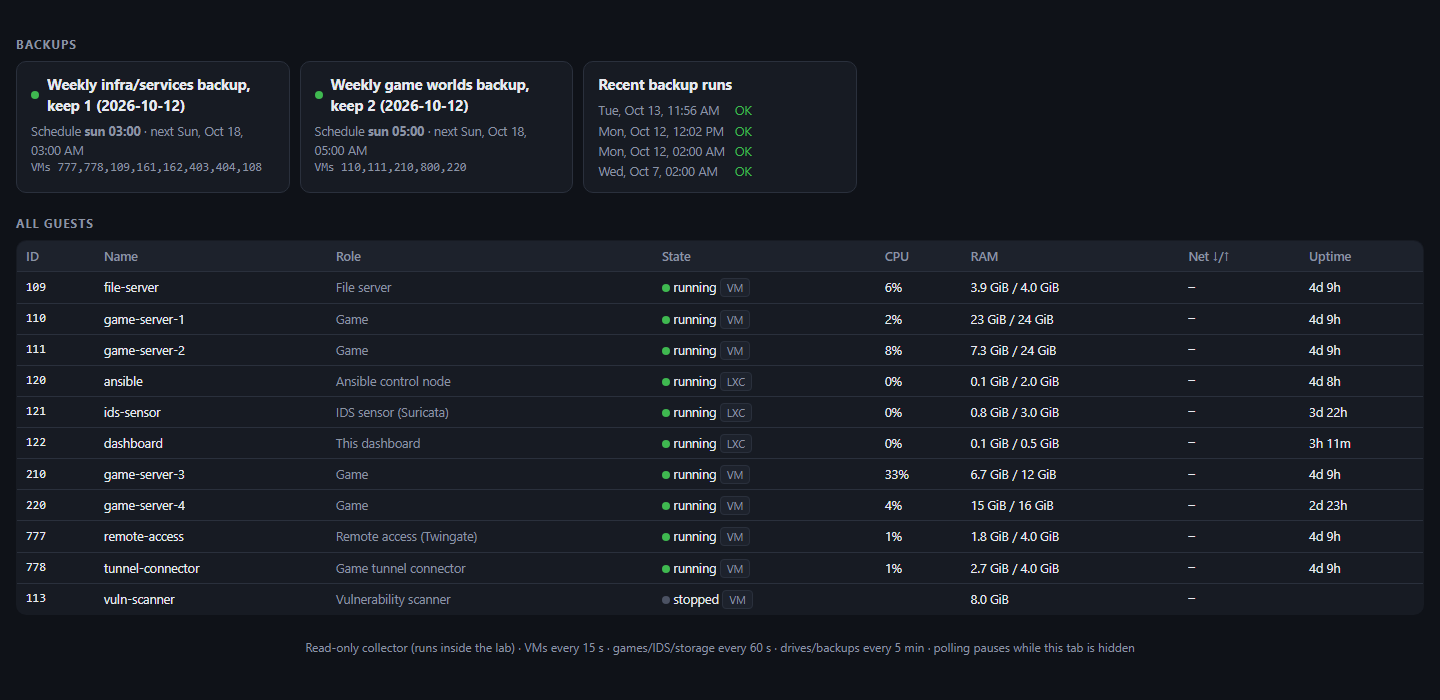
Same dashboard: the weekly backup jobs, recent runs, and everything running right now.
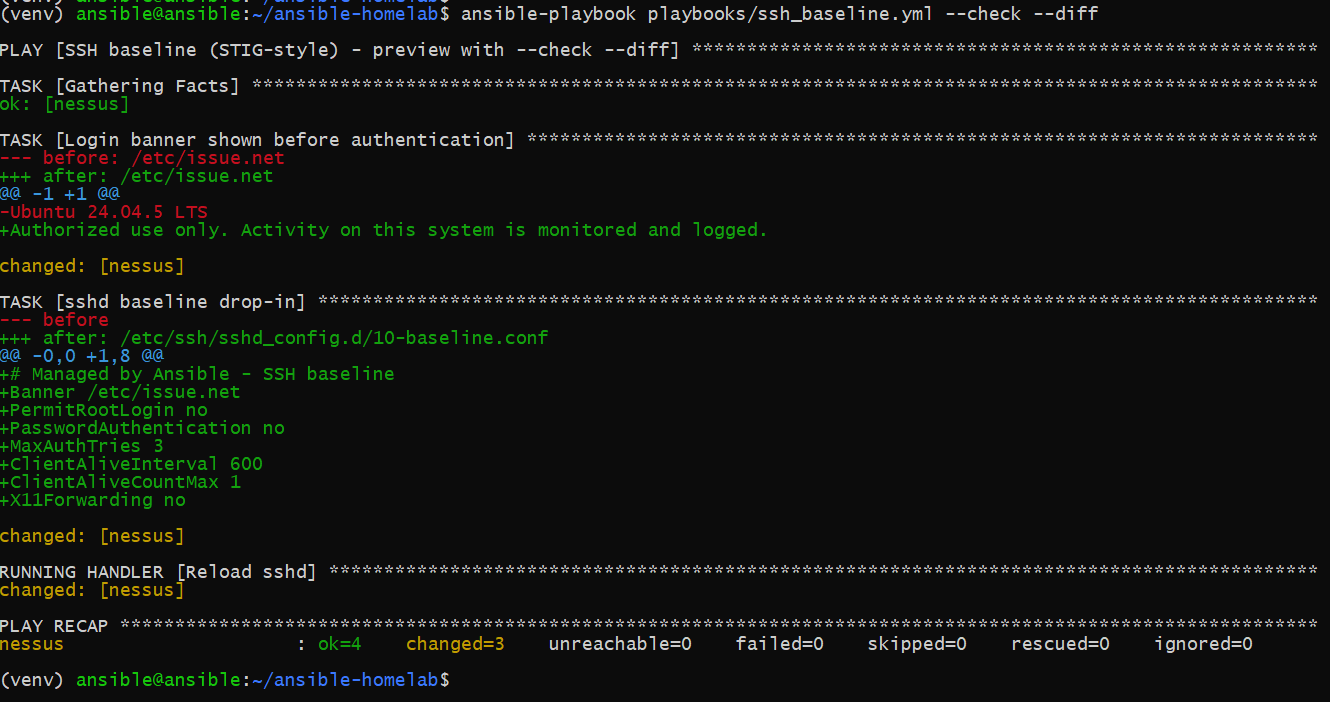
Ansible SSH baseline run in check mode: the exact diff (login banner + hardened sshd settings) shows up before anything changes. Dry run first, then apply.
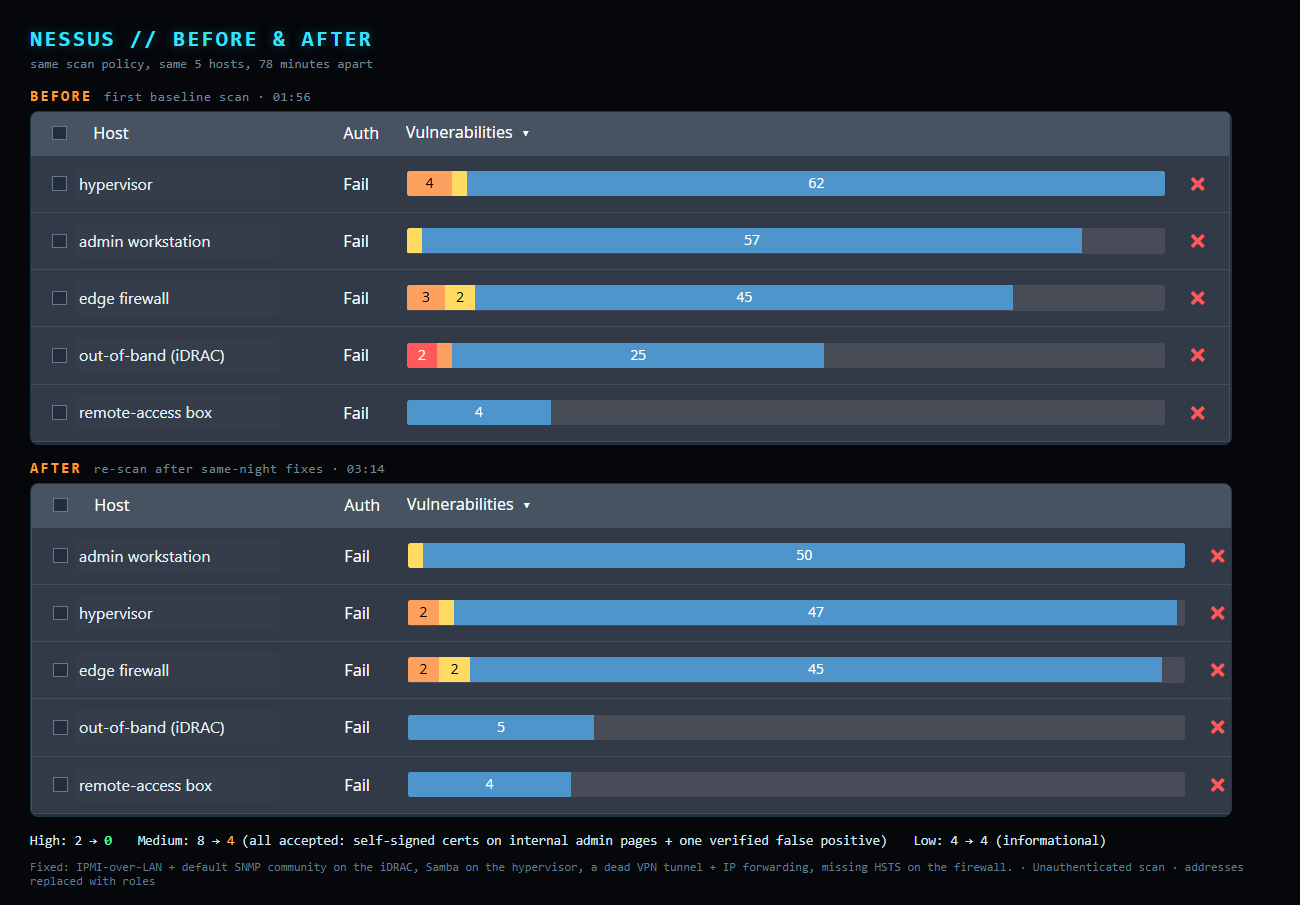
My first Nessus baseline found two highs on the server's out-of-band controller (IPMI hash disclosure, default SNMP community) plus an unneeded file-sharing service and a forgotten VPN on the hypervisor. Fixed the same night and re-scanned: highs 2 to 0. What's left is accepted risk (self-signed certs on internal admin pages). Addresses replaced with roles.